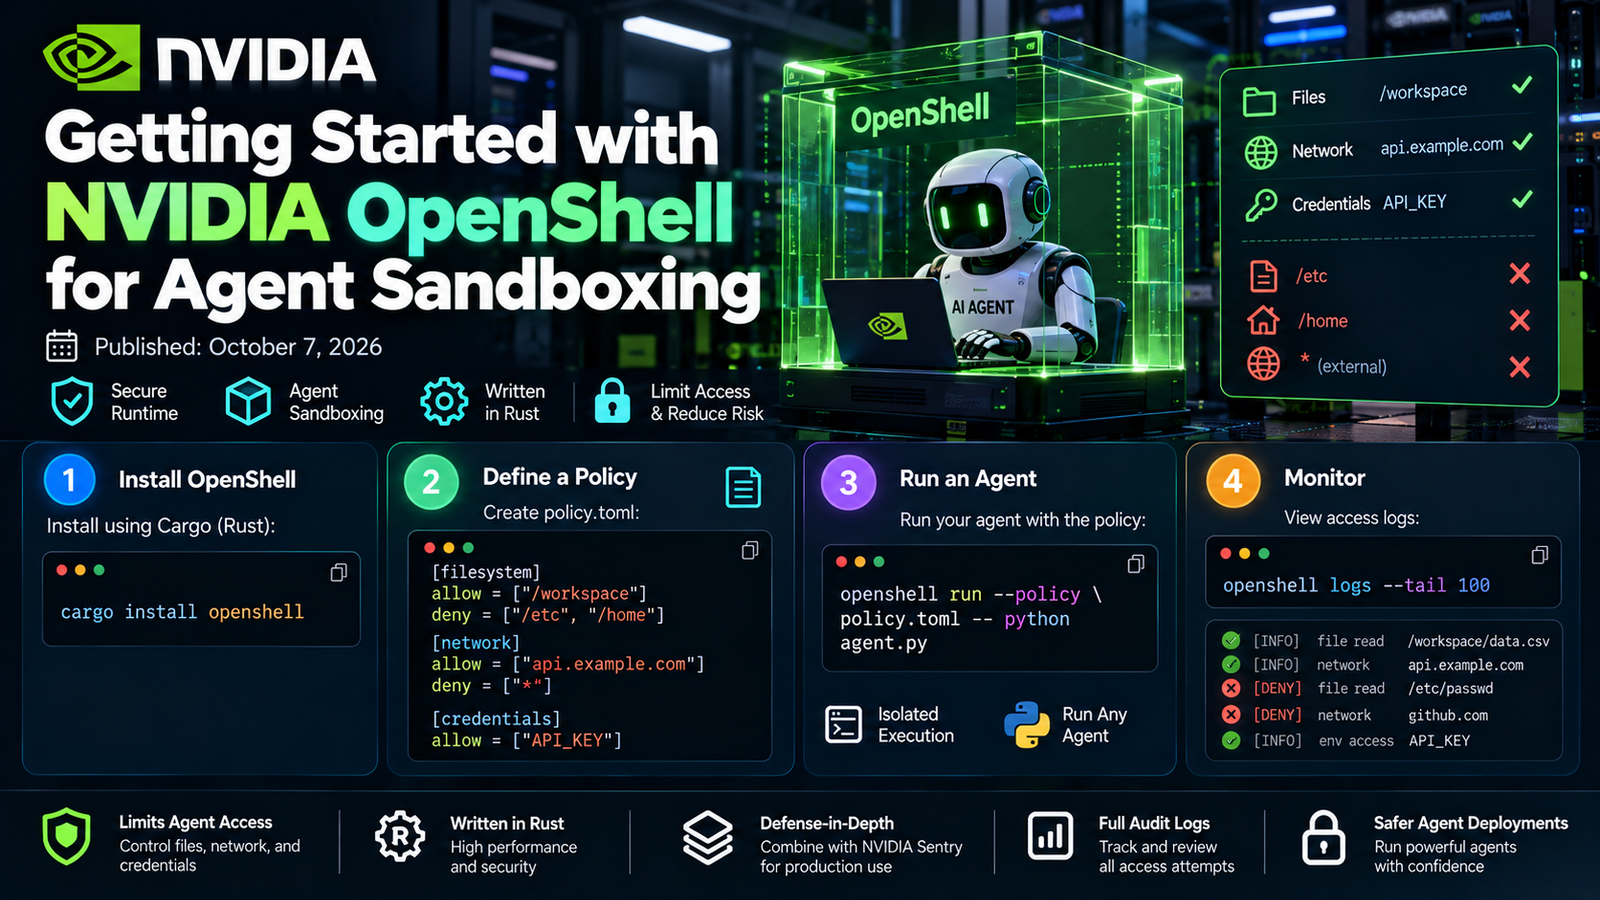
Getting Started with NVIDIA OpenShell for Agent Sandboxing
Published: October 7, 2026
OpenShell is NVIDIA's secure private runtime for autonomous AI agents, written in Rust.
Why Sandboxing Matters
Agents need access to files, tools, and credentials to be useful — but that access creates risk. OpenShell limits what agents can touch.
Step 1: Install
cargo install openshell
Step 2: Define a Policy
Create policy.toml:
[filesystem]
allow = ["/workspace"]
deny = ["/etc", "/home"]

[network]
allow = ["api.example.com"]
deny = ["*"]

[credentials]
allow = ["API_KEY"]
Step 3: Run an Agent
openshell run --policy policy.toml -- python agent.py
Step 4: Monitor
OpenShell logs all access attempts. Review them with:
openshell logs --tail 100
Conclusion
OpenShell provides defense-in-depth for agent deployments. Combine it with hardware watchdogs like NVIDIA Sentry for production use.
Tutorial based on public documentation.